


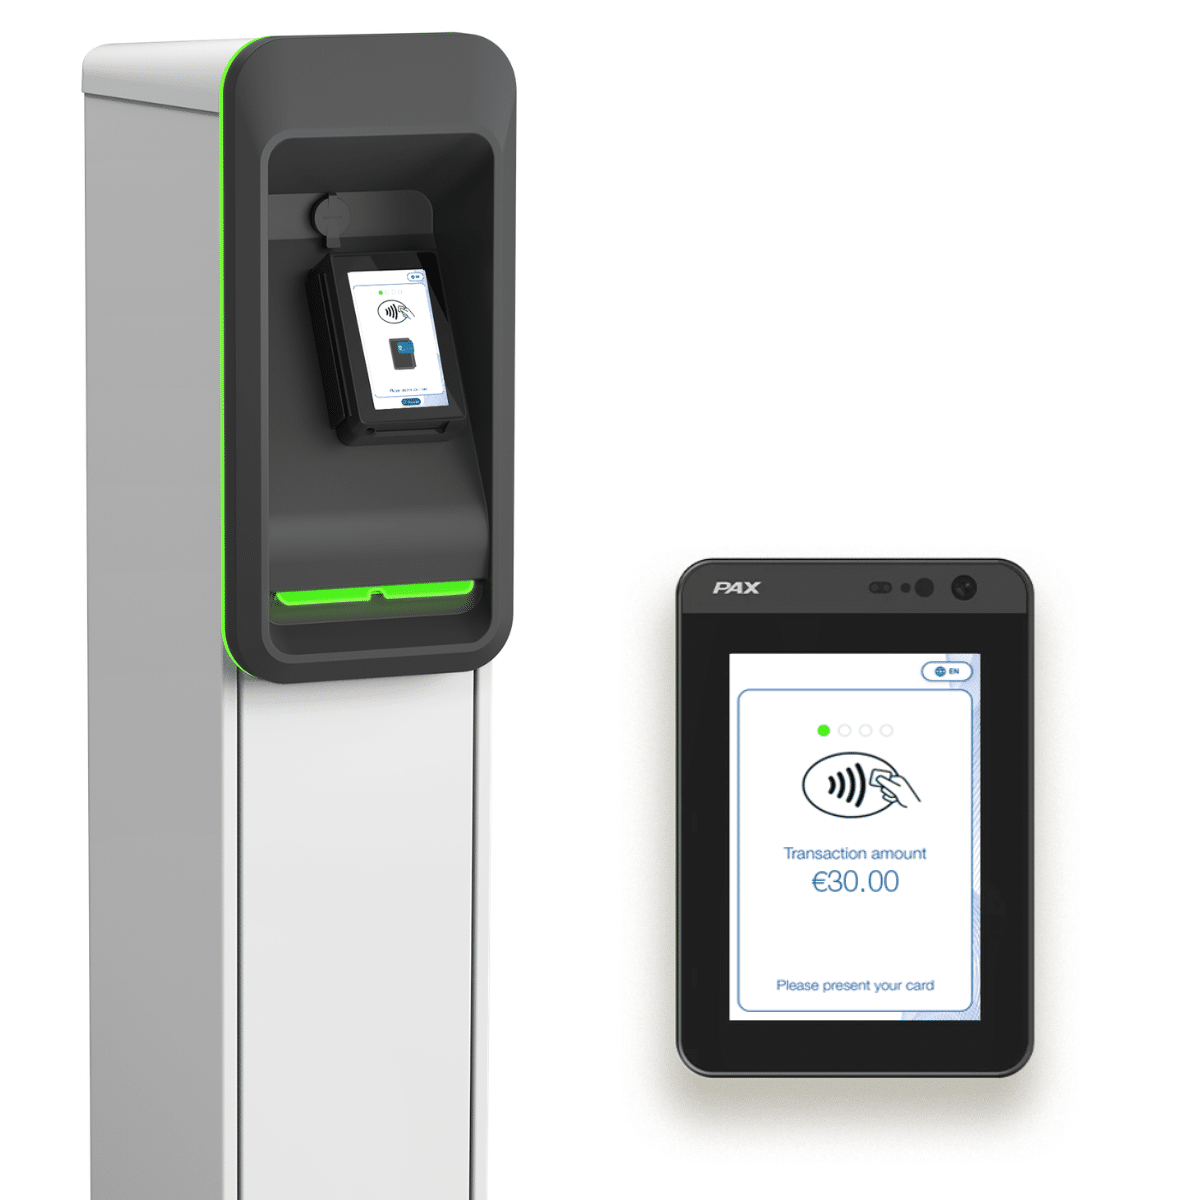
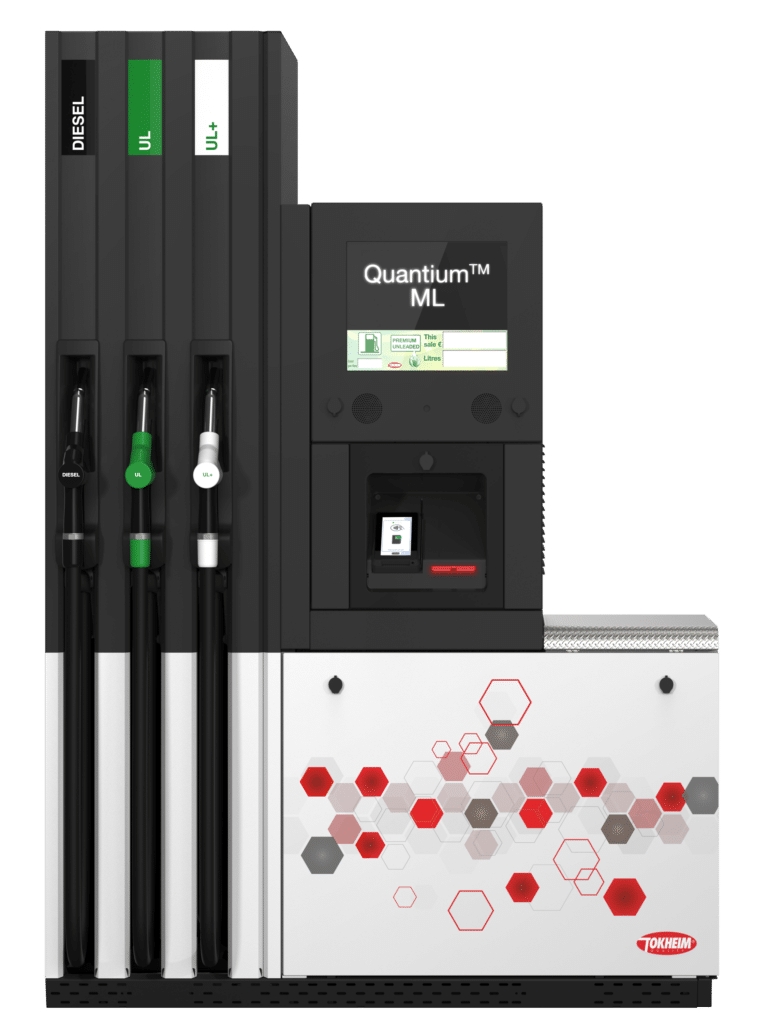
A terminal standing on its own out on the forecourt is exactly the kind of place where fraudsters try to fit a skimmer or tamper with the card reader. If that happens, it isn't only your customers' card data at risk. It's their trust in your site as well. That is why security in Crypto NOVA is built in from the start, not added afterwards.
Approved to PCI PTS 6.x with SRED
PCI PTS is the standard the card industry uses to approve terminals that read cards and PINs. Crypto NOVA is approved to version 6.x with SRED (Secure Reading and Exchange of Data). That means card data is protected from the moment the card is read, not somewhere further down the line.
Card data is encrypted straight away
NOVA encrypts card data in real time (P2PE, point-to-point encryption), so the details stay encrypted all the way from the terminal onwards. Behind the terminal sits Tokheim OASE™, which is itself certified to PCI DSS and PCI P2PE. Together, that means there are no readable card numbers on the site for anyone to steal.
Protection against skimming and tampering in the hardware itself
Protection against skimming and tampering is part of the terminal's design. It isn't an extra layer that can be forgotten or switched off, and it's there from the day the terminal goes in.
What it means for you
With card data encrypted from the terminal and all the way through OASE, it becomes easier to meet the requirements of PCI DSS. And because OASE handles card authorisation, you can change acquirer later without replacing the equipment on site.

